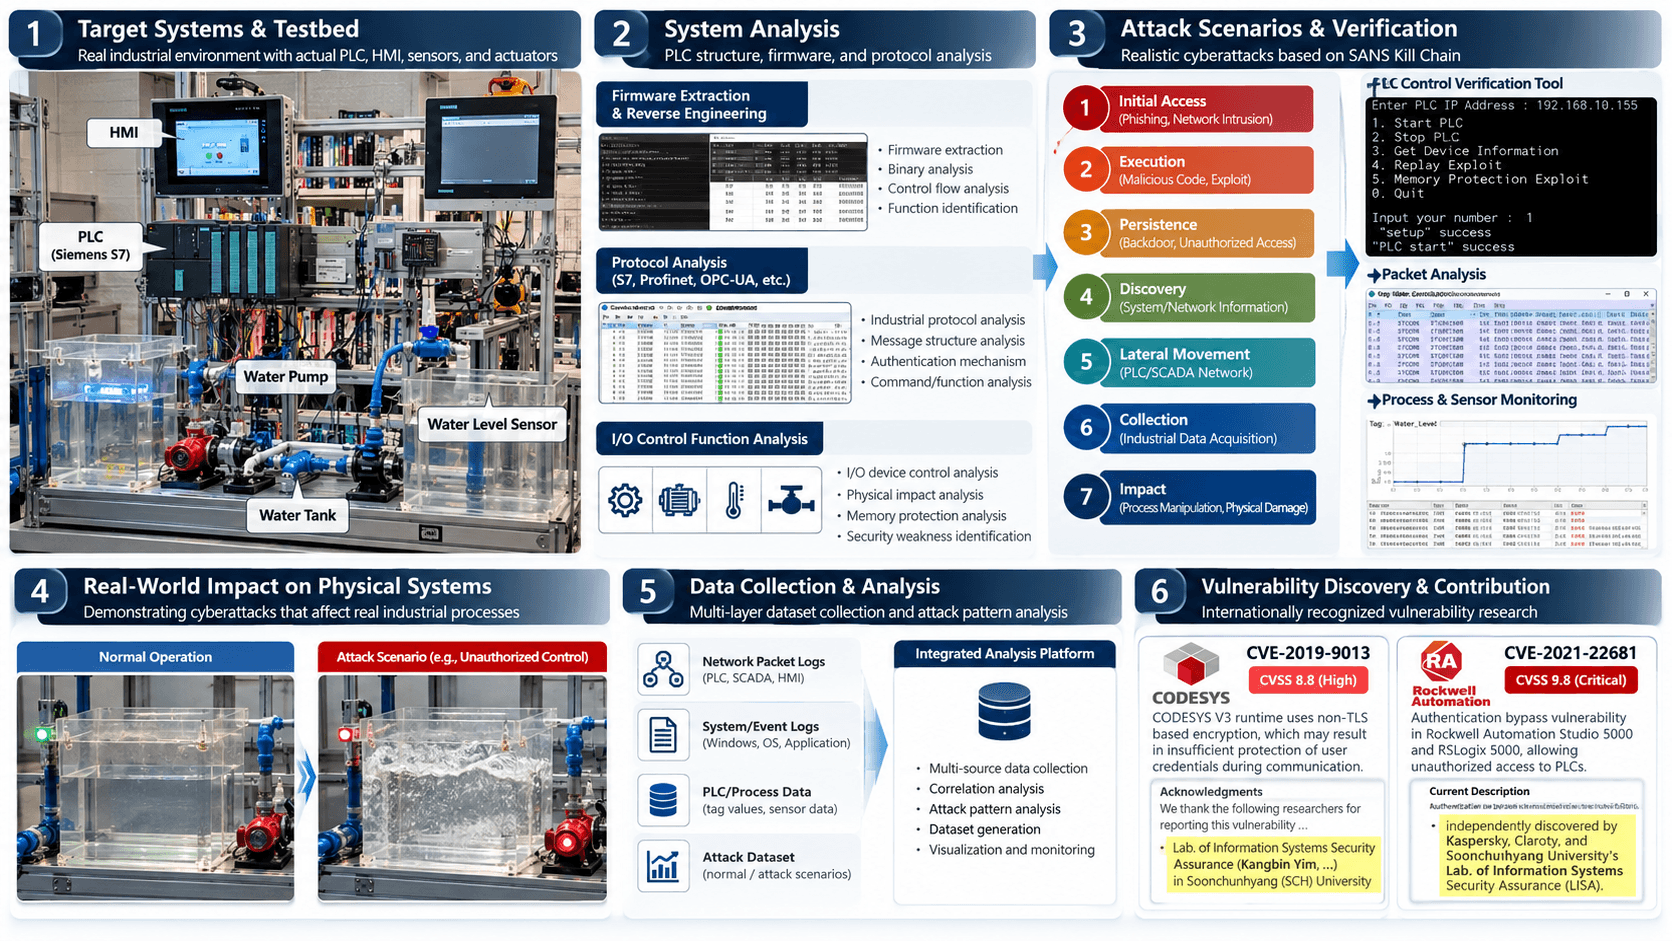
Industrial Control System (ICS) Cybersecurity: Vulnerability Analysis and Cyber-Physical Testbed Development
Industrial Control System (ICS) Cybersecurity: Vulnerability Analysis and Cyber-Physical Testbed Development
Securing Industrial Systems from Software Vulnerabilities to Physical Consequences
Industrial Control Systems (ICS) form the backbone of critical infrastructure, including manufacturing facilities, energy systems, and water treatment plants. Unlike conventional IT systems, cyberattacks against industrial environments can directly affect physical processes, potentially disrupting operations, damaging equipment, and compromising safety.
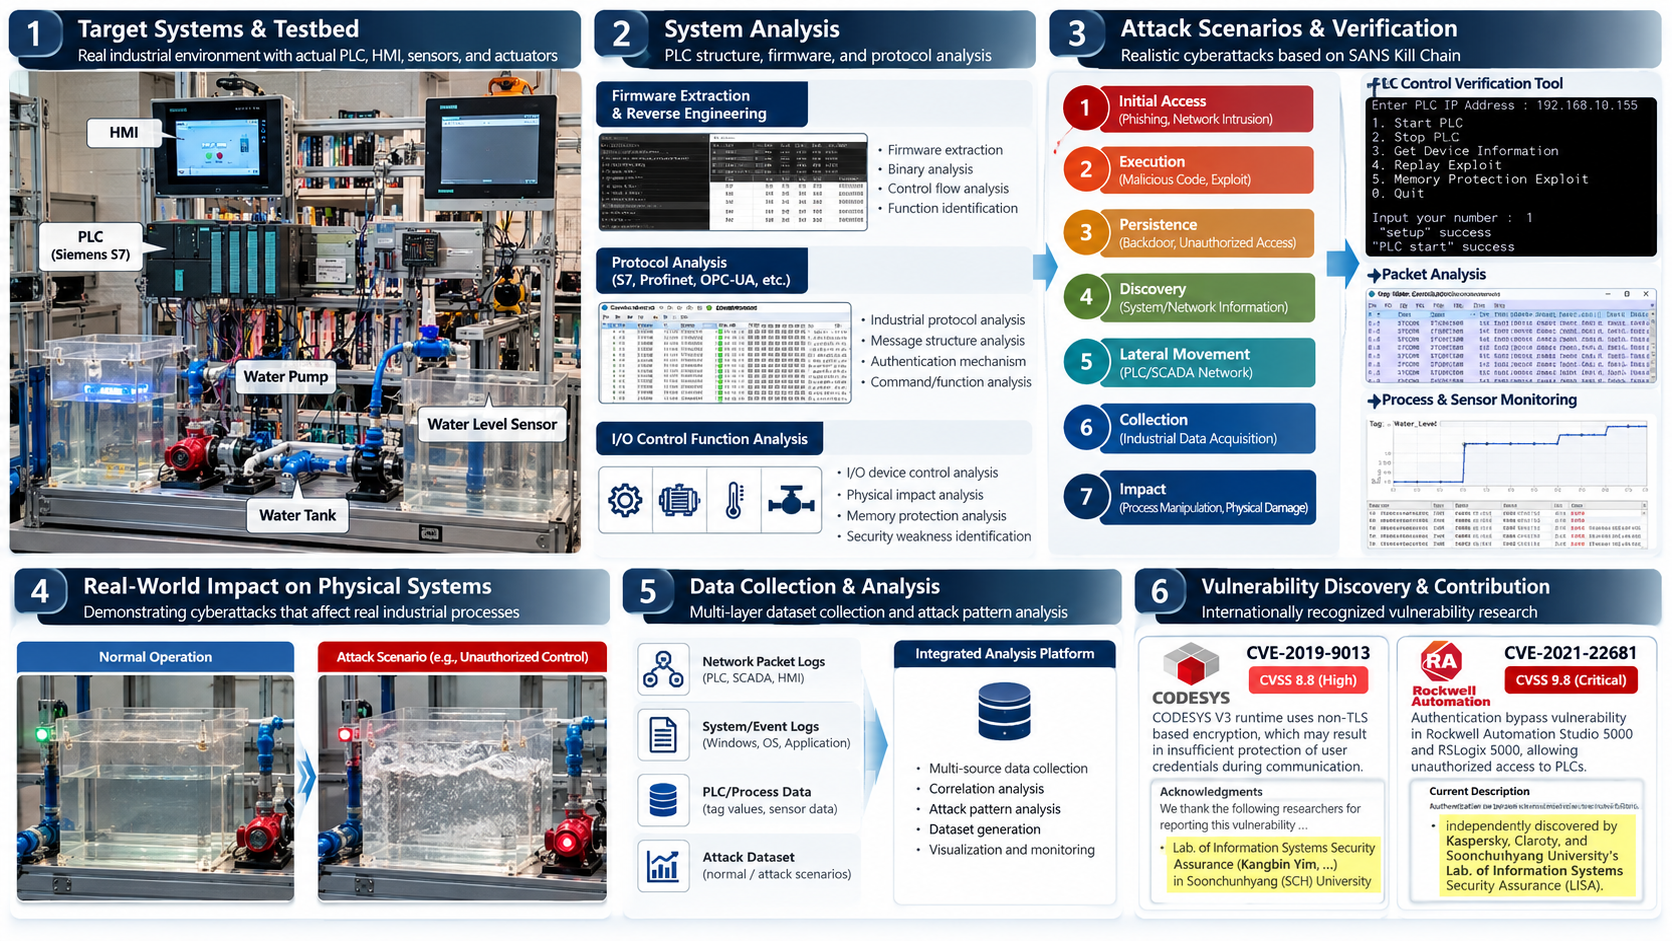
To address these challenges, LISA conducts comprehensive Industrial Control System security research, focusing on vulnerability identification, industrial communication protocol analysis, and cyber-physical attack verification using real industrial controllers.
PLC Vulnerability Analysis and Security Verification
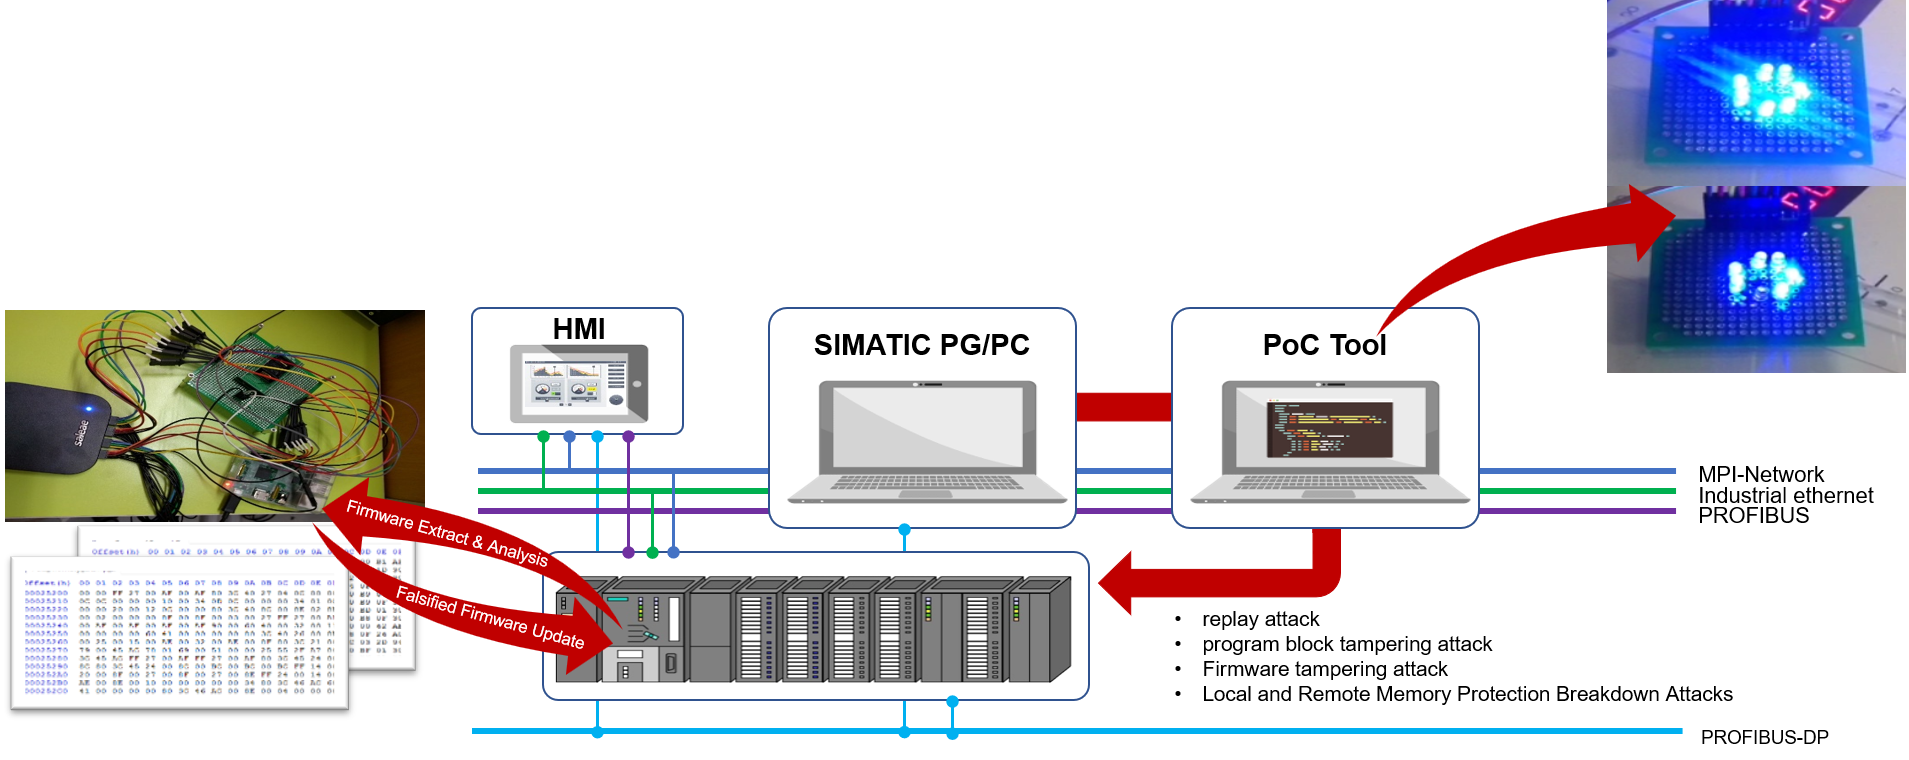
Our research investigates Programmable Logic Controllers (PLCs), particularly Siemens S7 systems, through structural analysis, firmware extraction, reverse engineering, and industrial communication protocol analysis.
By examining PLC control flows, memory protection mechanisms, authentication procedures, and device communication, LISA develops proof-of-concept (PoC) tools to identify and verify security weaknesses.
The research includes practical demonstrations of PLC start/stop manipulation, unauthorized device information access, replay attacks, and memory protection vulnerabilities, helping researchers understand how cyberattacks may influence industrial control operations.
Real-World ICS Testbed Development
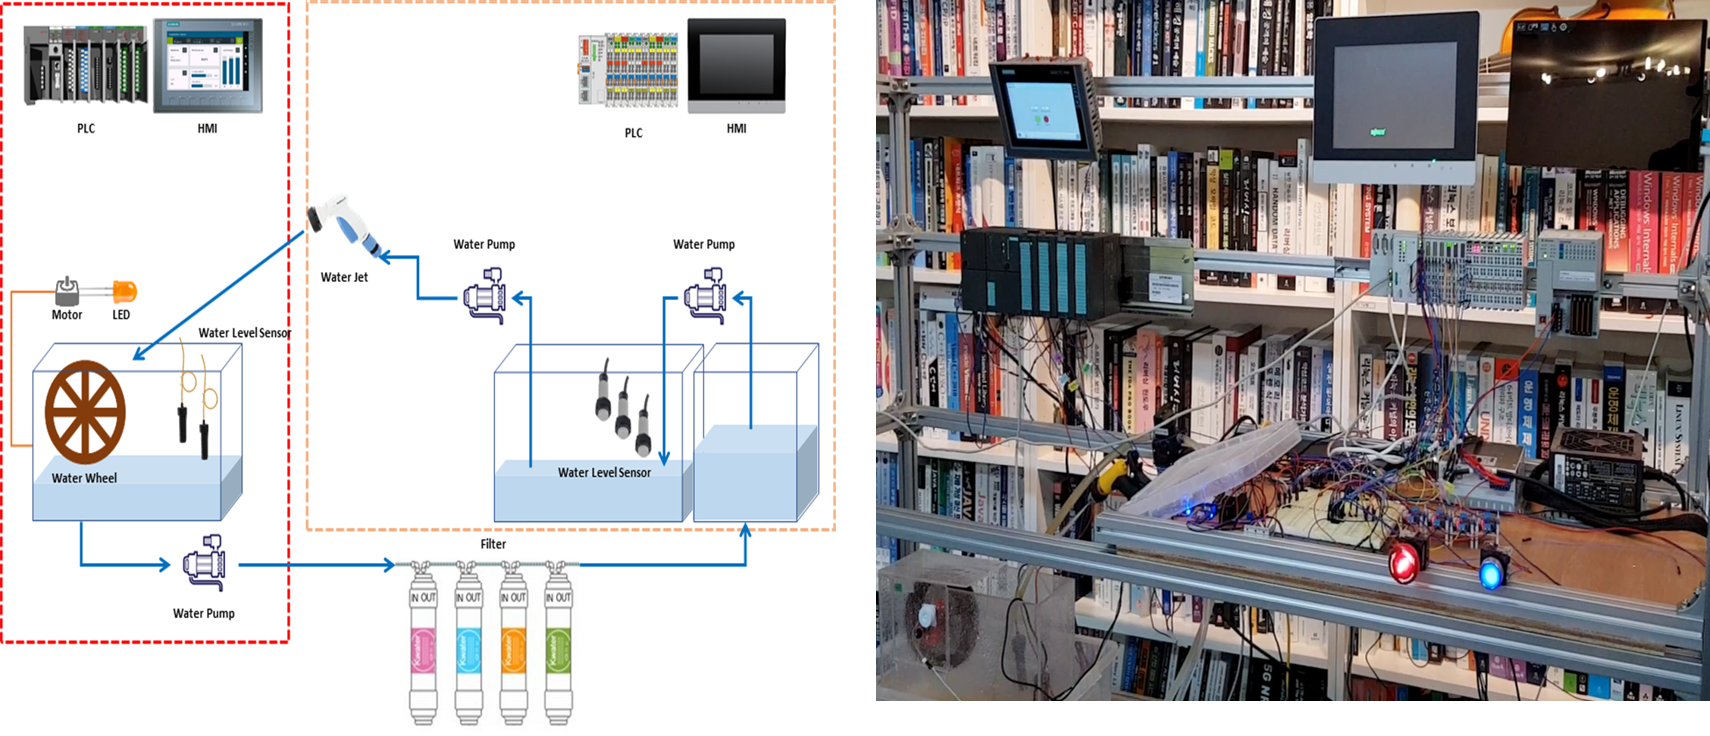
Beyond theoretical vulnerability analysis, LISA has designed and implemented physical ICS security testbeds integrating actual PLCs, Human-Machine Interfaces (HMIs), sensors, actuators, and industrial communication networks.
These testbeds reproduce industrial processes such as water circulation and level monitoring, allowing researchers to investigate how manipulated controller commands and communication messages affect physical system behavior.
By connecting cyberattack experiments with observable physical re
sponses, the framework enables controlled vulnerability verification, attack scenario reproduction, and security evaluation without exposing operational industrial facilities to unnecessary risks.
Multi-Layer Threat Analysis Based on Cyber Kill Chains
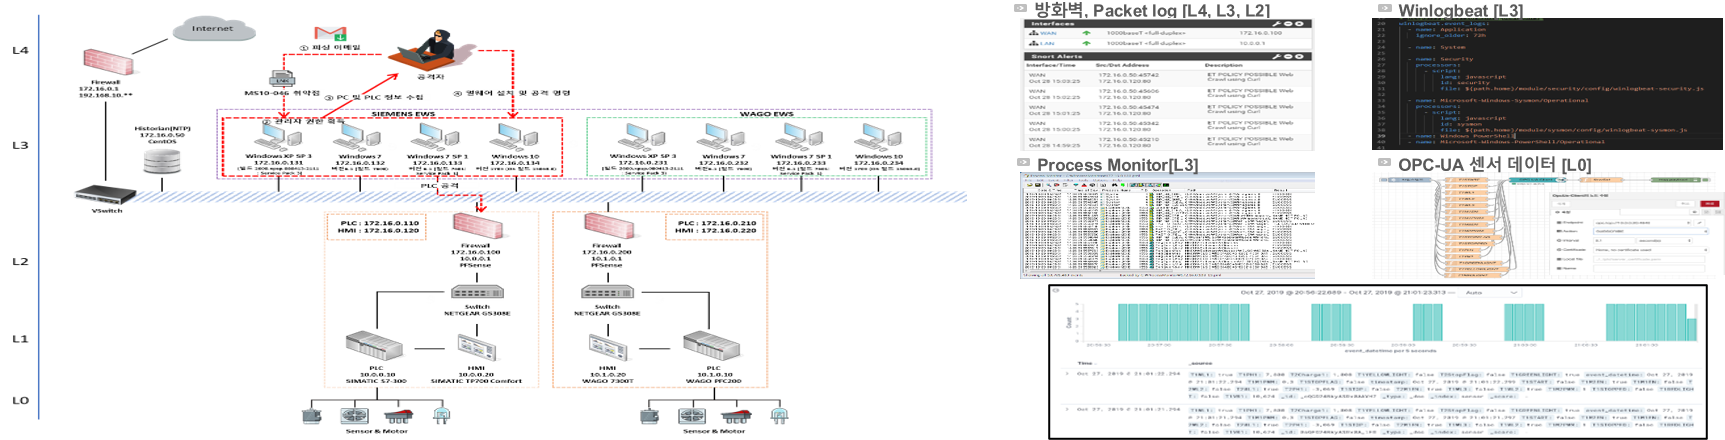
To investigate complex cyberattacks targeting industrial environments, LISA developed a multi-layer security analysis approach based on cyber kill-chain scenarios.
The framework collects and correlates security information across different industrial system layers, including network packet logs, operating system events, PLC communication, and OPC-UA sensor measurements.
By analyzing these heterogeneous datasets, researchers can investigate how threats progress from initial network access toward industrial process manipulation and examine relationships between cyber events and physical consequences.
Internationally Recognized Vulnerability Discoveries
LISA's research has contributed to the discovery and coordinated disclosure of significant vulnerabilities in widely deployed industrial automation technologies.
CVE-2019-9013 — CODESYS Runtime Security Vulnerability
LISA researchers were acknowledged in the CODESYS manufacturer's security advisory covering vulnerabilities in the CODESYS V3 runtime environment. CVE-2019-9013 concerns insufficient protection of user credentials during communication, potentially exposing industrial controllers to unauthorized access risks.
CVE-2021-22681 — Rockwell Automation Authentication Bypass
LISA researchers independently co-discovered a critical authentication bypass vulnerability affecting Rockwell Automation's Studio 5000, RSLogix 5000, and associated Logix controllers. The vulnerability could allow unauthorized applications to authenticate with industrial controllers and potentially modify controller configurations or application code.
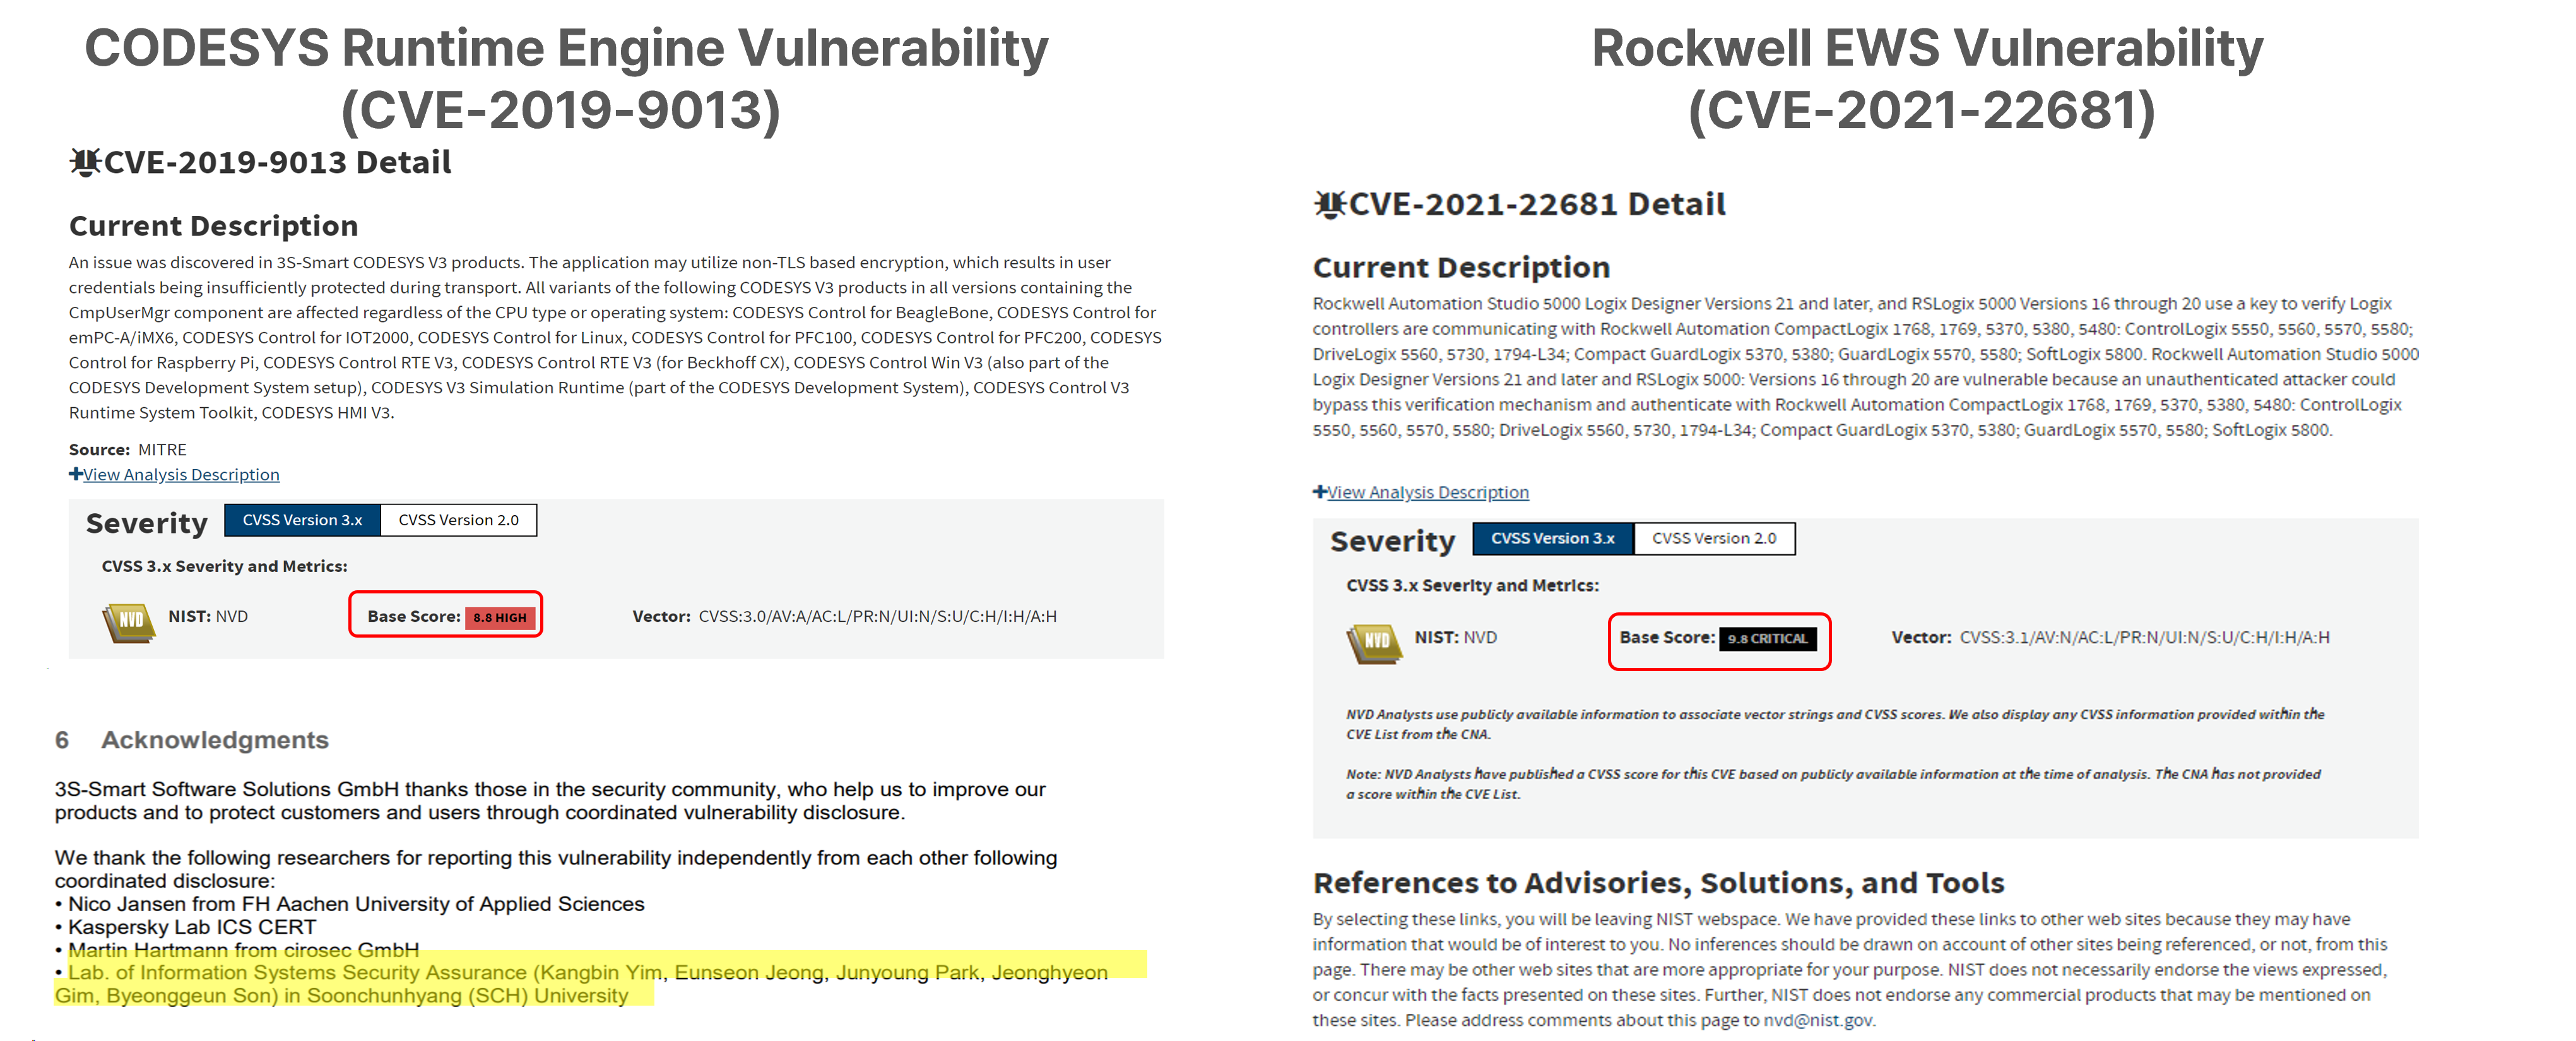
These discoveries demonstrate LISA's capabilities in identifying real-world industrial security weaknesses and contributing to coordinated vulnerability disclosure with international industrial cybersecurity researchers and manufacturers.